1942
US Patent 2,292,387, filed on 10 June 1941 and granted on 11 August 1942, described a radio guidance link for torpedoes that hopped between carrier frequencies in step at transmitter and receiver to resist jamming. The US Navy did not adopt it during the war.
1983
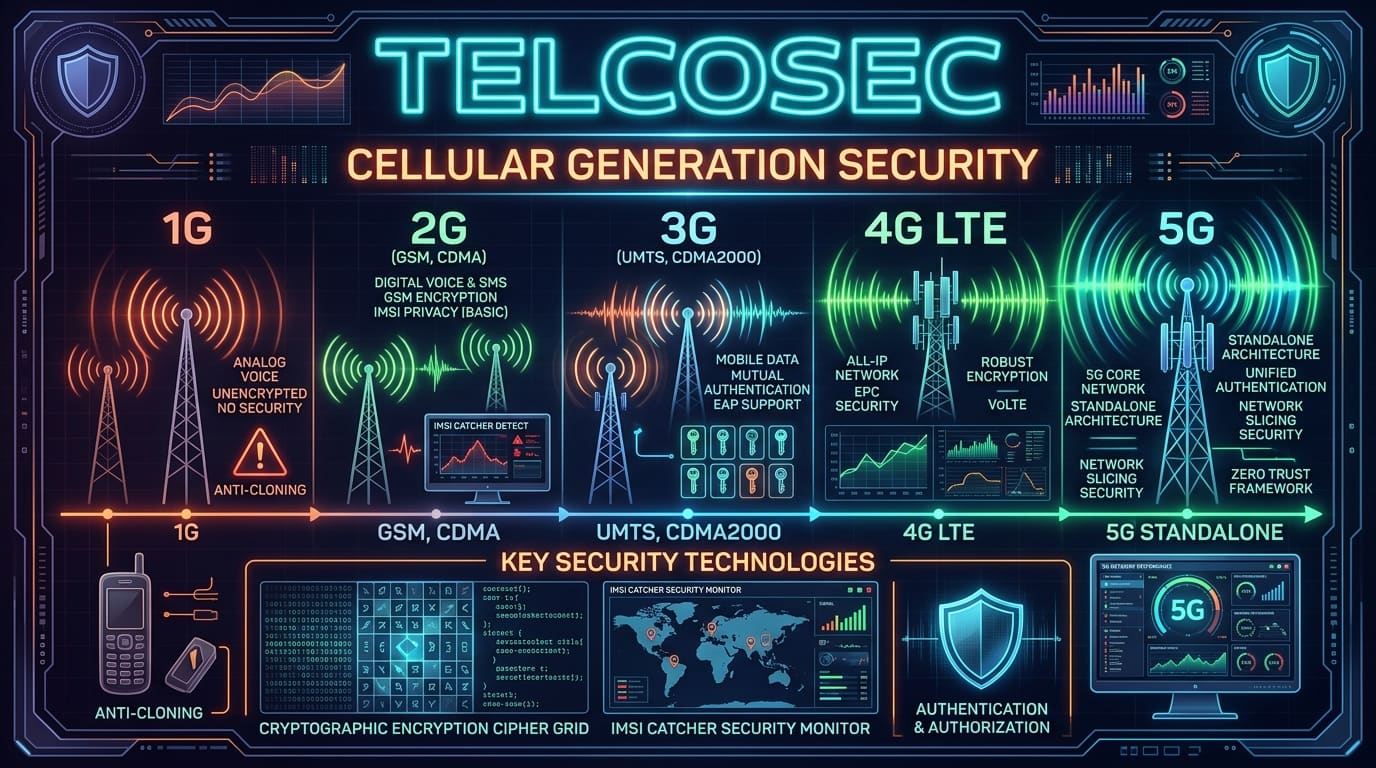
Ameritech launched the first commercial 1G AMPS cellular network in Chicago, but cleartext transmission of ESN and MIN identifiers quickly led to widespread over-the-air cellular cloning.
1991
The European Telecommunications Standards Institute (ETSI) deployed 2G GSM, introducing digital subscriber identity modules (SIM cards) and the A5/1 stream cipher for over-the-air voice privacy.
1997
Underground syndicates commercialized "Clone King" EPROM modification kits, allowing widespread cellular subscription fraud and free international calls across North American carriers.
1998
David Wagner and Ian Goldberg (UC Berkeley ISAAC Group) completely cracked the GSM COMP128-1 algorithm, allowing extraction of SIM master keys (Ki) and physical cloning of SIM cards.
2001
3GPP Release 99 standardized 3G UMTS, introducing bidirectional mutual authentication (3G AKA) to defeat rogue base stations (IMSI catchers) and replacing A5/1 with the KASUMI block cipher.
2003
Elad Barkan, Eli Biham and Nathan Keller of the Technion presented "Instant Ciphertext-Only Cryptanalysis of GSM Encrypted Communication" at CRYPTO 2003, recovering the A5/2 session key in less than a second on a PC from a few dozen milliseconds of encrypted over-the-air traffic.
2004
In June 2004 F-Secure analysed Cabir, a proof-of-concept worm linked to the 29A virus-writing group and the first known worm for mobile phones, which spread between Symbian Series 60 handsets over Bluetooth; in March 2005 CommWarrior added self-propagation over operator MMS.
2009
Karsten Nohl and the Chaos Computer Club published a 2-terabyte rainbow-table set at 26C3 enabling real-time over-the-air decryption of A5/1-protected 2G GSM calls and SMS with inexpensive hardware.
2010
At 27C3 (December 2010), Harald Welte and Steve Markgraf presented OsmocomBB, a free GSM baseband stack for cheap Calypso phones, while Karsten Nohl and Sylvain Munaut used such phones to capture and decrypt GSM calls with about $15 of consumer hardware.
2015
Joshua Drake of Zimperium zLabs disclosed in July 2015 a set of critical memory-corruption flaws in Android's Stagefright media library — CVE-2015-1538 plus the related CVE-2015-1539, CVE-2015-3824, CVE-2015-3826, CVE-2015-3827, CVE-2015-3828, CVE-2015-3829 and CVE-2015-3864 — that let an attacker run code on an estimated 950 million phones via a single silently received MMS video.
2018
At ACM CCS 2018 (Toronto, October 2018), Basin, Dreier, Hirschi, Radomirović, Sasse and Stettler presented the first comprehensive formal model of 3GPP 5G AKA and showed several critical security goals are not met without assumptions missing from the standard.
2018
In June 2018, researchers from Ruhr University Bochum and NYU Abu Dhabi (Rupprecht, Kohls, Holz, Pöpper) disclosed that LTE user-plane traffic is encrypted but not integrity-protected, allowing a nearby man-in-the-middle relay to redirect a victim's DNS traffic.
2020
5G Standalone (Release 16, 2020) replaced SS7/Diameter trust assumptions with HTTP/2 service-based APIs over TLS, OAuth 2.0 token authentication, and cryptographically concealed subscriber identities (SUCI).
2026
3GPP SA3 is preparing to migrate 5G and future 6G security to post-quantum cryptography. After the Release 19 cryptographic inventory (TR 33.938), the Release 20 study TR 33.703 evaluates options built on NIST FIPS 203 (ML-KEM) and FIPS 204 (ML-DSA), published in August 2024, and a Release 20 normative work item, Post-quantum Cryptography Migration Phase 1, is under way. No PQC scheme has yet been standardized for SUCI.